Blog

Information and insight on today's advanced threats from the leader in advanced threat prevention.

All Posts


Update: Ad Vulna Continues

This is an update to our earlier blog “Ad Vulna: A Vulnaggressive (Vulnerable & Aggressive) Adware Threatening Millions”.

Since our last notification to Google and Ad Vulna (code name for anonymity), we have noticed a number of changes to the impacted apps that we reported to both companies. We summarize our observations below, although we do not have specific information about the reasons that caused these changes we are reporting.

First, a number of these vulnaggressive apps and their developers’ accounts have been removed from Google Play, such as app developer “Itch Mania”. The total number of downloads of these apps was more than 6 million before the removal. While removing these apps from Google Play prevents more people from being affected, the millions of devices that already downloaded them remain vulnerable. Continue reading »

ASLR Bypass Apocalypse in Recent Zero-Day Exploits

ASLR (Address Space Layout Randomization) is one of the most effective protection mechanisms in modern operation systems. But it’s not perfect. Many recent APT attacks have used innovative techniques to bypass ASLR.

Here are just a few interesting bypass techniques that we have tracked in the past year:

  • Using non-ASLR modules
  • Modifying the BSTR length/null terminator
  • Modifying the Array object

The following sections explain each of these techniques in detail.

Continue reading »

“Be the Change.” Test Methodologies for Advanced Threat Prevention Products

Organizations are under assault by a new generation of cyber attacks that easily evade traditional defenses. These coordinated campaigns are targeted. They are stealthy. And they are persistent. Many exploit zero-day vulnerabilities and orchestrate attacks across multiple vectors (Web, email, file, mobile). The threat actors are dead set on finding an organization’s weaknesses, finding their way into the systems, and stealing intellectual property. Guarding against these advanced threats necessitates, nay demands, a fundamentally different approach to threat defense. Importantly, this is even more true for testing methodologies used to validate the efficacy of these products. This is because legacy test methodologies were developed to test the efficacy of legacy security products that are signature-based and designed to detect known malware and known vulnerabilities – not the advanced threat landscape!

Before we define a good test methodology for advanced security products, it is important to establish what advanced security products must do - for only when we know what the products must accomplish will we know how to test them.

Continue reading »

Ad Vulna: A Vulnaggressive (Vulnerable & Aggressive) Adware Threatening Millions

FireEye researchers have discovered a rapidly-growing class of mobile threats represented by a popular ad library affecting apps with over 200 million downloads in total. This ad library, anonymized as “Vulna,” is aggressive at collecting sensitive data and is able to perform dangerous operations such as downloading and running new components on demand. Vulna is also plagued with various classes of vulnerabilities that enable attackers to turn Vulna’s aggressive behaviors against users. We coined the term “vulnaggressive” to describe this class of vulnerable and aggressive characteristics. Most vulnaggresive libraries are proprietary and it is hard for app developers to know their underlying security issues. Legitimate apps using vulnaggressive libraries present serious threats for enterprise customers. FireEye has informed both Google and the vendor of Vulna about the security issues and they are actively addressing it.

Recently FireEye discovered a new mobile threat from a popular ad library that no other anti-virus or security vendor has reported publicly before. Mobile ad libraries are third-party software included by host apps in order to display ads. Because this library’s functionality and vulnerabilities can be used to conduct large-scale attacks on millions of users, we refer to it anonymously by the code name “Vulna” rather than revealing its identity in this blog. Continue reading »

Another Darkleech Campaign

Last week got us up close and personal with Darkleech and Blackhole with our external careers web site compromise as described here:

https://www.fireeyesolution.com/blog/technical/cyber-exploits/2013/09/darkleech-says-hello.html

The fun didn’t end there, this week we saw a tidal wave of Darkleech activity linked to a large-scale malvertising campaign identified by the following URL:

hXXp://delivery[.]globalcdnnode[.]com/7f01baa99716452bda5bba0572c58be9/afr-zone.php

Again Darkleech was up to its tricks, injecting URLs and sending victims to a landing page belonging to the Blackhole Exploit Kit, one of the most popular and effective exploit kits available today. Blackhole wreaks havoc on computers by exploiting vulnerabilities in client applications like IE, Java and Adobe, computers that are vulnerable to exploits launched by Blackhole are likely to become infected with one of several flavors of malware including ransomware, Zeus/Zbot variants and clickfraud trojans like ZeroAccess.

We started logging hits at 21:31:00 UTC on Sunday 09/22/2013, the campaign has been ongoing, peaking Monday and tapered down through out the week.

During most of the campaign’s run, delivery[.]globalcdnnode[.]com appeared to have gone dark, no longer serving the exploit kit’s landing page as expected and then stopped resolving altogether, yet tons of requests kept flowing.

This left some scratching their heads as to whether the noise was a real threat.

Continue reading »

Hand Me Downs: Exploit and Infrastructure Reuse Among APT Campaigns

Since we first reported on Operation DeputyDog, at least three other Advanced Persistent Threat (APT) campaigns known as Web2Crew, Taidoor, and th3bug have made use of the same exploit to deliver their own payloads to their own targets. It is not uncommon for APT groups to hand-off exploits to others, who are lower on the zero-day food chain – especially after the exploit becomes publicly available. Thus, while the exploit may be the same, the APT groups using them are not otherwise related.

In addition, APT campaigns may reuse existing infrastructure for new attacks. There have been reports that the use of CVE-2013-3893 may have begun in July; however, this determination appears to be based solely on the fact that the CnC infrastructure used in DeputyDog had been previously used by the attackers. We have found no indication that the attackers used CVE-2013-3893 prior to August 23, 2013.

Continue reading »

Needle in a Haystack: Detecting Zero-Day Attacks

People often ask me what differentiates FireEye from its rivals. The real question is “What should I look for in a solution to advanced persistent threats, regardless of the provider?” (And while I can rattle off a long list of reasons why FireEye should be that provider, I’ll save that for another time.)

The key for any solution to advanced persistent threats (APTs) is finding the needle in the haystack — detecting and blocking zero-day incidents from among millions of traffic flows in a typical enterprise network. That means detecting it accurately, with few false positives or false negatives. Attackers, especially the well-funded ones, invest lots of time up front designing attacks to avoid detection and enhance impact. By accurately identifying their targets and the best way to approach them (often by analyzing social networks), attackers maximize their impact while minimizing chances of detection.

To combat persistent attackers, solutions must become smarter. When evaluating any advanced threat prevention solution, the three key issue to consider are accuracy, scale, and timeliness of detection. Continue reading »

New FireEye Report: World War C

National security decision makers need to know – is cyber war fact or fiction? When the theater of operations is invisible, hype may be our single greatest enemy.

Cyber war skeptics raise valid points, such as the current known number of human casualties caused by cyber attacks: zero. But … that’s not the end of the story, because we are only at the beginning of the Internet era.

It is true that computer hacking is a technical discipline, not a death ray. But as such, computer hacking is best understood not as an end in itself, but a potentially powerful means to a wide variety of political, military, and economic goals. Continue reading »

Now You See Me - H-worm by Houdini

H-worm is a VBS (Visual Basic Script) based RAT written by an individual going by the name Houdini. We believe the author is based in Algeria and has connections to njq8, the author of njw0rm [1] and njRAT/LV [2] through means of a shared or common code base. We have seen the H-worm RAT being employed in targeted attacks against the international energy industry; however, we also see it being employed in a wider context as run of the mill attacks through spammed email attachments and malicious links.

The Payload

The H-worm payload is simply a VBS file, which is often wrapped, in a PE executable dropper. The H-worm VBS file is also packed with multiple layers of obfuscation in some cases. While analyzing such samples (81c153256efd9161f4d89fe5fd7015bc and 4543daa6936dde54dda8782b89d5daf1), we discovered that they were obfuscated with custom Base64 encoding, multiple levels of standard Base64 encoding (Safa Crypter), and character substitutions. The obfuscation techniques used have been described here [3] already and are summarized in Figure 1 below. There is also an Autoit version of H-worm called the “underworld version” floating around which has the same functionality as the VBS version.

Continue reading »

Operation DeputyDog Part 2: Zero-Day Exploit Analysis (CVE-2013-3893)

In our previous blog post my colleagues Ned and Nart provided a detailed analysis on the Advanced Persistent Threat (APT) Campaign Operation DeputyDog. The campaign leveraged a zero-day vulnerability of Microsoft Internet Explorer (CVE-2013-3893). Microsoft provided an advisory and ‘Fix it’ blog post.

I am happy to announce that Xiaobo Chen, a well-known security researcher, has recently joined FireEye Labs. We worked together on the analysis of this zero-day vulnerability. In this blog, we will provide a deep dive on the exploitation part of the campaign. Continue reading »

Threat Research


Filter by Category:


Black Hat USA Talks: Investigating PowerShell Attacks

Threat actors are always eager to adopt new tools, tactics, and procedures that can help them evade detection and conduct their mission. Incident responders from Mandiant have observed increasing use of PowerShell by targeted attackers to conduct command-and-control in compromised Windows networks. As a trusted administration tool built-in to all modern versions of Windows, PowerShell provides the ability to access remote systems, execute commands, transfer files, load malicious code, and interact with underlying components of the operating system – all tasks for which attackers must otherwise rely on malware. This has created a whole new playground of intrusion techniques for intruders that have already established a foothold on systems in a corporate network.

Ryan Kazanciyan and Matt Hastings will talk about the use of PowerShell throughout the attack lifecycle and the sources of evidence it leaves behind in memory, on disk, in logs, and elsewhere. They will demonstrate how to collect and interpret these forensic artifacts, both on individual systems and at scale. Throughout the presentation, they will include examples from real-world incidents.

Attend this presentation on August 7 at 4:05pm PT in South Seas GH. Make sure to use #BHUSA and @FireEye if you plan to tweet highlights from the talk.

To view the whitepaper, click here.

Black Hat USA Talks: Sidewinder Targeted Attack Against Android in The Golden Age of Ad Libs

While Google Play has little malware, many vulnerabilities exist in the apps as well as the Android system itself, and aggressive ad libs leak a lot of user privacy information. When they are combined together, more powerful targeted attacks can be conducted.

In this presentation, FireEye’s Yulong Zhang and Tao Wei will present one practical case of such attacks called “Sidewinder Targeted Attack.” It targets victims by intercepting location information reported from ad libs, which can be used to locate targeted areas such as a CEO’s office or some specific conference rooms. When the target is identified, “Sidewinder Targeted Attack” exploits popular vulnerabilities in ad libs, such as Javascript-binding-over-HTTP or dynamic-loading-over-HTTP, etc.

During the exploit, it is a well-known challenge to call Android services from injected native code due to the lack of Android application context. So they will also demonstrate how attackers can invoke Android services such as taking photos, calling phone numbers, sending SMS, reading/writing the clipboard, etc. Once intruding into the target, the attackers can exploit several Android vulnerabilities to get valuable privacy information or initiate more advanced attacks. We will reveal how to exploit new vulnerabilities we discovered in this phase.

In addition, they will show demos using real-world apps downloaded from Google Play.

Although they notified Google, ad vendors and app developers about related issues half a year ago, there are still millions of users under the threat of “Sidewinder Targeted Attacks” due to the slow patching/upgrading/fragmentation of the Android ecosystem.

Attend this presentation on August 7 at 10:15am PT in South Seas GH. Make sure to use #BHUSA and @FireEye if you plan to tweet highlights from the talk.

To view the whitepaper, click here.

Black Hat USA Talks - Leviathan: Command And Control Communications On Planet Earth

Every day, computer network attackers leverage a Leviathan of compromised infrastructure, based in every corner of the globe, to play hide-and-seek with network security, law enforcement, and counterintelligence personnel.

This presentation draws a new map of Planet Earth, based not on traditional parameters, but on hacker command and control (C2) communications. The primary data points used in this worldwide cyber survey are more than 30 million malware callbacks to over 200 countries and territories over an 18-month period, from January 2013 to June 2014.

First, this talk covers the techniques that hackers use to communicate with compromised infrastructure across the globe. The authors analyze the domains, protocols, ports, and websites used for malicious C2. They explain how covert C2 works, and how attackers keep their communications hidden from network security personnel.

Second, this talk looks at strategic impact. The authors examine relationships between the targeted industries and countries and the first-stage malware servers communicating with them. Traffic analysis is used to deduce important relationships, patterns, and trends in the data. This section correlates C2 communications to traditional geopolitical conflicts and considers whether computer network activity can be used to predict real world events.

In conclusion, the authors consider the future of this Leviathan, including whether governments can subdue it – and whether they would even want to.

Attend this presentation on August 7 at 10:15am PT in South Seas GH. Make sure to use #BHUSA and @FireEye if you plan to tweet highlights from the talk.

To view the whitepaper, click here.

Operation Poisoned Hurricane

Introduction

Our worldwide sensor network provides researchers at FireEye Labs with unique opportunities to detect innovative tactics employed by malicious actors and protects our clients from these tactics. We recently uncovered a coordinated campaign targeting Internet infrastructure providers, a media organization, a financial services company, and an Asian government organization. The actor responsible for this campaign utilized legitimate digital certificates to sign their tools and employed innovative techniques to cloak their command and control traffic.

Hurricane Electric Redirection

In March of 2014, we detected Kaba (aka PlugX or SOGU) callback traffic to legitimate domains and IP addresses. Our initial conclusion was that this traffic was the result of malicious actors ‘sleeping’ their implants, by pointing their command and control domains at legitimate IP addresses. As this is a popular technique, we did not think much of this traffic at the time.

Further analysis revealed that the HTTP headers of the traffic in question contained a Host: entry for legitimate domains. As we have previously observed malware families that forge their HTTP headers to include legitimate domains in callback traffic, we concluded that the malware in this case was configured in the same way.

An example of the observed traffic is as follows:

POST /C542BB084F927229348B2A34 HTTP/1.1
Accept: */*
CG100: 0
CG103: 0
CG107: 61456
CG108: 1
User-Agent: Mozilla/4.0 (compatible; MSIE 9.0; Windows NT 6.1; SLCC2; .NET CLR 2.0.50727; .NET CLR 3.5.30729; .NET CLR 3.0.30729; Media Center PC 6.0; .NET4.0C)
Host: www.adobe.com
Content-Length: 0
Cache-Control: no-cache

As we continued to see this odd traffic throughout the summer we began a search for malware samples responsible for this behavior. Via this research, we found a malware sample that we believe was responsible for at least some of the strange traffic that we had observed. The identified sample had the following properties:

MD5: 52d2d1ab9b84303a585fb81e927b9e01
Size: 180296
Compile Time: 2013-10-15 05:17:37
Import Hash: b29eb78c7ec3f0e89bdd79e3f027c029
.rdata: d7b6e412ba892e9751f845432625bbb0
.text: ed0dd6825e3536d878f39009a7777edc
.data: 1bc25d2f0f3123bedea254ea7446dd50
.rsrc: 91484aa628cc64dc8eba867a8493c859
.reloc: f1df8fa77b5abb94563d5d97e5ccb8e2
RT_VERSION: 9dd9b7c184069135c23560f8fbaa829adc7af6d2047cf5742b5a1e7c5c923cb9

This sample was signed with a legitimate digital certificate from the ‘Police Mutual Aid Association’. This certificate has a serial number of ‘06 55 69 a3 e2 61 40 91 28 a4 0a ff a9 0d 6d 10’.

Analysis of this Kaba sample revealed that it was configured to directly connect to both www.adobe.com and update.adobe.com. Obviously, this configuration does not make a lot of sense, as the actor would not be able to control their implants from anywhere on the Internet since they did not have direct control over these domains – unless the attackers were able to re-route traffic destined for these domains from specific victims. Indeed, further analysis of this Kaba variant revealed that it was also configured to use specific DNS resolvers. This sample was configured to resolve DNS lookups via Hurricane Electric’s nameservers of 216.218.130.2, 216.218.131.2, 216.218.132.2 and 216.66.1.2.

We found this interesting, so we investigated how these Hurricane Electric’s nameservers were configured. Subsequently, we found that anyone could register for a free account with Hurricane Electric’s hosted DNS service. Via this service, anyone with an account was able to register a zone and create A records for the registered zone and point those A records to any IP address they so desired. The dangerous aspect of this service is that anyone was able to hijack legitimate domains such as adobe.com. Although these nameservers are not recursors and were not designed to be queried directly by end users, they were returning results if queried directly for domains that were configured via Hurricane Electrics public DNS service. Furthermore, Hurricane Electric did not check if zones created by their users were already been registered or are otherwise legitimately owned by other parties.

As we continued this research, we identified 21 legitimate fully qualified domain names that had been hijacked via this technique by at least one APT actor. In addition to the adobe.com domain mentioned above, another one of the poisoned domains is www.outlook.com. A lookup of this domain via Google’s DNS resolvers returns expected results:

$ dig +short @8.8.8.8 www.outlook.com
www.outlook.com.glbdns2.microsoft.com.
www-nameast.outlook.com.
157.56.240.246
157.56.236.102
157.56.240.214
157.56.241.102
157.56.232.182
157.56.241.118
157.56.240.22

A quick lookup of these addresses reveal that Microsoft owns them:

157.56.240.246 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.236.102 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.240.214 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.241.102 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.232.182 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.241.118 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION
157.56.240.22 | 8075 | 157.56.0.0/16 | MICROSOFT-CORP-MSN-A | US | MICROSOFT.COM | MICROSOFT CORPORATION

However, as recently as August 4, 2014 a lookup of the same www.outlook.com domain via Hurricane Electric’s resolvers returned entirely different results[1]:

$ dig +short @216.218.130.2 www.outlook.com
59.125.42.167

$ dig +short @216.218.131.2 www.outlook.com
59.125.42.167

$ dig +short @216.218.132.2 www.outlook.com
59.125.42.167

$ dig +short @216.66.1.2 www.outlook.com
59.125.42.167

$ whois -h asn.shadowserver.org ‘origin 59.125.42.167′
3462 | 59.125.0.0/17 | HINET | TW | HINET.NET | DATA COMMUNICATION BUSINESS GROUP

Passive DNS research on the 59.125.42.167 IP address revealed that multiple APT actors have previously used this IP address.

IP Address Domain First Seen Last Seen
59.125.42.167 ml65556.gicp[.]net 2014-06-23 2014-07-23
59.125.42.167 wf.edsplan[.]com 2014-05-12 2014-05-14
59.125.42.167 gl.edsplan[.]com 2014-05-12 2014-05-14
59.125.42.167 unix.edsplan[.]com 2014-05-12 2014-05-14

Additional researched uncovered more Kaba samples that were configured to leverage Hurricane Electric’s public DNS resolvers. Another sample has the following properties:

MD5: eae0391e92a913e757ac78b14a6f079f
Size: 184304
Compile Time: 2013-11-26 17:39:25
Import Hash: f749528b1db6fe5aee61970813c7bc18
Text Entry: 558bec83ec1056ff7508ff1518b00010
.rdata: 747abda5b3cd3494f056ab4345a909e4
.text: 475c20b8abc972710941ad6659492047
.data: d461f8f7b3f35b7c6855add6ae59e806
.rsrc: b195f57cb5e605cb719469492d9fe717
.reloc: d6b23cb71f214d33e56cf8f6a10c0c10
RT_VERSION: 9dd9b7c184069135c23560f8fbaa829adc7af6d2047cf5742b5a1e7c5c923cb9

This sample is signed with a recently expired digital certificate from ‘MOCOMSYS INC’. This certificate has a serial number of ‘03 e5 a0 10 b0 5c 92 87 f8 23 c2 58 5f 54 7b 80’.

This sample used Hurricane Electric’s public DNS resolvers to route traffic to the hijacked domains of www.adobe.com and update.adobe.com. We also noted that this sample was configured to connect directly to 59.125.42.168 – one IP address away from the IP that received traffic from the hijacked www.outlook.com domain.

Passive DNS research revealed that this IP hosted the same set of known APT domains listed above:

IP Address Domain First Seen Last Seen
59.125.42.168 ml65556.gicp[.]net 2014-04-23 2014-07-24
59.125.42.168 wf.edsplan[.]com 2014-04-23 2014-05-14
59.125.42.168 gl.edsplan[.]com 2014-05-04 2014-05-14
59.125.42.168 unix.edsplan[.]com 2014-05-04 2014-05-14

While this problem does not directly impact users of www.adobe.com, www.outlook.com, or users of the other affected domains, it should not be dismissed as inconsequential. Actors that adopt this tactic and obfuscate the destination of their traffic through localized DNS hijacks can significantly complicate the job of network defenders.

Via our sensor network, we observed the actor responsible for this activity conducting a focused campaign. We observed this actor target:

  • Multiple Internet Infrastructure Service Providers in Asia and the United States
  • A Media Organization based in the United States
  • A financial institution based in Asia
  • An Asian government organization

Google Code Command and Control

Furthermore, we also discovered this same actor conducting a parallel campaign that leveraged Google Code for command and control. On August 1, 2014 we observed a malicious self-extracting executable (aka sfxrar) file downloaded from 211.125.81.203. This file had the following properties:

MD5: 17bc9d2a640da75db6cbb66e5898feb1
Size: 282800 bytes

A valid certificate from ‘QTI INTERNATIONAL INC’ was used to sign this sfxrar. This certificate had a serial number of ‘2e df b9 fd cf a0 0c cb 5a b0 09 ee 3a db 97 b9’. The sfxrar contained the following files:

File Size MD5
msi.dll 11680 029c8f56dd89ceeaf928c3148d13eba7
msi.dll.dat 115218 62834d2c967003ba5284663b61ac85b5
setup.exe 34424 d00b3169f45e74bb22a1cd684341b14a

Setup.exe is a legitimate executable from Kaspersky used to load the Kaba (aka PlugX) files – msi.dll and msi.dll.dat.

google-code17

These Kaba files are configured to connect to Google Code – specifically code.google.com/p/udom/. On August 1, this Google Code project contained the encoded command “DZKSGAAALLBACDCDCDOCBDCDCDOCCDADIDOCBDADDZJS”.

def NewPlugx_C2_redir_decode(s):

rvalue = “”
for x in range(0, len(s), 2):
tmp0 = (ord(s[x+1]) - 0×41) << 4

rvalue += chr(ord(s[x]) + tmp0 - 0×41)
return rvalue

The command ‘DZKSGAAALLBACDCDCDOCBDCDCDOCCDADIDOCBDADDZJS’ decodes to 222.122.208.10. In a live environment, the Kaba implant would then connect to this IP address via UDP.

Further analysis of project at code.google.com/p/udom/ revealed the project owner, 0x916ftb691u, created a number of other projects. We decoded the commands hosted at these linked projects and found that they issued the following decoded commands:

112.175.143.22
59.125.42.167
153.121.57.213
61.82.71.10
202.181.133.169
61.78.32.139
61.78.32.148
202.181.133.216
59.125.42.168
119.205.217.104
222.122.208.10
112.175.143.16
222.122.208.9
27.122.13.204

It is likely that other yet to be discovered Kaba variants are configured to connect to these related Google Code projects and then redirect to this list of IP addresses.

Passive DNS analysis of these IP addresses revealed connections to the following known malicious infrastructure:

IP Address Domain First Seen Last Seen
27.122.13.204 bq.cppcp[.]com 2014-03-21 2014-05-08
112.175.143.16 uj.verisignss[.]com 2013-06-30 2013-08-13
112.175.143.16 www.verifyss[.]com 2013-06-30 2013-07-22
112.175.143.16 uj.byonds[.]com 2013-06-24 2013-07-22
112.175.143.16 uj.verifyss[.]com 2013-06-30 2013-07-22
59.125.42.168 ml65556.gicp[.]net 2014-04-23 2014-07-24
59.125.42.168 wf.edsplan[.]com 2014-04-23 2014-05-14
59.125.42.168 gl.edsplan[.]com 2014-05-04 2014-05-14
59.125.42.168 unix.edsplan[.]com 2014-05-04 2014-05-14
59.125.42.167 ml65556.gicp[.]net 2014-06-23 2014-07-23
59.125.42.167 wf.edsplan[.]com 2014-05-12 2014-05-14
59.125.42.167 gl.edsplan[.]com 2014-05-12 2014-05-14
59.125.42.167 unix.edsplan[.]com 2014-05-12 2014-05-14
61.78.32.148 door.nexoncorp[.]com 2014-04-30 2014-06-22
61.78.32.148 verisignss[.]com 2014-04-30 2014-06-22
61.78.32.148 th.nexoncorp[.]com 2014-04-30 2014-06-22
61.78.32.148 tw.verisignss[.]com 2014-04-30 2014-06-22
61.78.32.148 sd.nexoncorp[.]com 2014-04-30 2014-06-22
61.78.32.148 mail.nexoncorp[.]com 2014-04-30 2014-06-22
112.175.143.22 door.nexoncorp[.]com 2014-04-01 2014-04-30
112.175.143.22 th.nexoncorp[.]com 2014-04-01 2014-04-30
112.175.143.22 sd.nexoncorp[.]com 2014-04-01 2014-04-30
112.175.143.22 mail.nexoncorp[.]com 2014-04-01 2014-04-30
112.175.143.22 verisignss[.]com 2013-12-29 2014-04-30
112.175.143.22 tw.verisignss[.]com 2013-12-29 2014-04-30

Relationships Between Campaigns

As mentioned above the Kaba variant eae0391e92a913e757ac78b14a6f079f shared a common import hash of f749528b1db6fe5aee61970813c7bc18 with many of the samples listed in this post. This samples was to use Hurricane Electric’s nameservers as well as connect directly to the IP address 59.125.42.168.

Note that we identified the same C2 IP 59.125.42.168 via our analysis of the malicious Google Code projects. Specifically, the Google Project at code.google.com/p/tempzz/, which is linked to the project at code.google.com/p/udom/, issued an encoded command that decoded to 59.125.42.168.

We also identified another related Kaba variant that connected to code.google.com/p/updata-server. This variant had the following properties:

MD5: 50af349c69ae4dec74bc41c581b82459
Size: 180600 bytes
Compile Time: 2014-04-01 03:28:31
Import Hash: f749528b1db6fe5aee61970813c7bc18
.rdata: 103beeefae47caa0a5265541437b03a1
.text: e7c4c2445e76bac81125b2a47384d83f
.data: 5216d6e6834913c6cc75f40c8f70cff8
.rsrc: b195f57cb5e605cb719469492d9fe717
.reloc: f7d9d69b8d36fee5a63f78cbd3238414
RT_VERSION: 9dd9b7c184069135c23560f8fbaa829adc7af6d2047cf5742b5a1e7c5c923cb9

This sample was signed with a valid digital certificate from ‘PIXELPLUS CO., LTD’ and had a serial number of ‘0f e7 df 6c 4b 9a 33 b8 3d 04 e2 3e 98 a7 7c ce’.

In addition to sharing the same Import hash of f749528b1db6fe5aee61970813c7bc18 seen in other samples listed throughout this post, 50af349c69ae4dec74bc41c581b82459 contained a RT_VERSION resource of 9dd9b7c184069135c23560f8fbaa829adc7af6d2047cf5742b5a1e7c5c923cb9. This same RT_VERSION was used in a number of other related samples including:

MD5 C2 Uses Hurricane Electric
7e6c8992026a79c080f88103f6a69d2c h.cppcp[.]comu.cppcp[.]com NO
52d2d1ab9b84303a585fb81e927b9e01 www.adobe[.]comupdate.adobe[.]com YES
787c6cf3cb18feeabe4227ec6b19db01 ns.lovechapelumc[.]orgns1.lovechapelumc[.]org NO

20140803-Sogu-TTPs

Conclusion

These coordinated campaigns demonstrate that APT actors are determined to continue operations. As computer network defenders increase their capabilities to identify and block these campaigns by deploying more advanced detection technologies, threat actors will continue to adopt creative evasion techniques.

We observed the following evasion techniques in these campaigns:

    • The use of legitimate digital certificates to sign malware
    • The use of Hurricane Electrics public DNS resolvers to redirect command and control traffic
    • The use of Google Code to obfuscate the location of command and control servers

While none of these techniques are necessarily new, in combination, they are certainly both creative and have been observed to be effective. Although the resultant C2 traffic can be successfully detected and tracked, the fact that the malware appears to beacon to legitimate domains may lull defenders into a false sense of security. Network defenders should continue to study the evolution of advanced threat actors, as these adversaries will continue to evolve in pursuit of their designated objectives.

Related MD5s
17bc9d2a640da75db6cbb66e5898feb1
eae0391e92a913e757ac78b14a6f079f
434b539489c588db90574a64f9ce781f
7e6c8992026a79c080f88103f6a69d2c
52d2d1ab9b84303a585fb81e927b9e01
787c6cf3cb18feeabe4227ec6b19db01
50af349c69ae4dec74bc41c581b82459
d51050cf98cc723f0173d1c058c12721

Digital Certificates
MOCOMSYS INC, (03 e5 a0 10 b0 5c 92 87 f8 23 c2 58 5f 54 7b 80)
PIXELPLUS CO., LTD., (0f e7 df 6c 4b 9a 33 b8 3d 04 e2 3e 98 a7 7c ce)
Police Mutual Aid Association (06 55 69 a3 e2 61 40 91 28 a4 0a ff a9 0d 6d 10)
QTI INTERNATIONAL INC (2e df b9 fd cf a0 0c cb 5a b0 09 ee 3a db 97 b9)
Ssangyong Motor Co. (1D 2B C8 46 D1 00 D8 FB 94 FA EA 4B 7B 5F D8 94)
jtc (72 B4 F5 66 7F 69 F5 43 21 A9 40 09 97 4C CC F8)

Footnotes
[1] As of August 4, 2014 Hurricane Electric was no longer returning answers for www.outlook.com or the other affected domains.
[2] This same encoding algorithm was previously described by Cassidian at http://blog.cassidiancybersecurity.com/post/2014/01/plugx-some-uncovered-points.html

Operation Arachnophobia: An Introduction

We recently had the opportunity to collaborate with ThreatConnect’s Intelligence Research Team (TCIRT) to conduct follow-up reporting on threat group activity that appears to originate from Pakistan. The TCIRT originally reported on this activity in August 2013 in their “Where There is Smoke, There is Fire” blog post. This post covered a threat group using malware and apparent lures that would be effective against Indian targets: an Indian Government Ministry of Defense pension memorandum and an apparent lure related to Sarabjit Singh, an Indian national who died in a Pakistani prison last year.

Our collaboration with ThreatConnect centered on technical analysis of the BITTERBUG malware family and other technical characteristics of the activity. ThreatConnect provided deep analysis of open source data to highlight interesting persona and organizational details. FireEye Labs analysts have also been tracking this group’s activities – identifying and tracking their custom malware family that we call BITTERBUG and their command and control (C2) servers.

The report was released today assessing new information on this group and identifying new factors that draw further suspicion to Pakistan as the probable origination point. From the earliest samples of BITTERBUG to its latest variants, we have observed changes that show movement away from specific debug paths to new, generic paths; a process that occurred following TCIRT’s original blog post.

The group appears to have remained active after the TCIRT blog post, using new BITTERBUG malware variants with the more-generic embedded file paths. During this same timeframe, we observed these variants packaged with various support components and using lures related to the December 2013 arrest of Indian diplomat Devyani Khobragade in the United States and the March 2014 disappearance of Malaysia Airlines flight 370 (cast in these ‘lure’ emails as a Pakistan-related hijacking). Though BITTERBUG deployment methods remained similar throughout, we also observed new deployment behaviors following the August blog post.

We encourage you to read the new paper here http://www.threatconnect.com/arachnophobia.

Security Perspective


Filter by Category:


Operation Poisoned Hurricane: Lessons for CISOs

The tactics described in “Operation Poisoned Hurricane” should come as a stark reminder that advanced threat actors do not stand still. They continue to refine their tradecraft, finding new and innovative ways to bypass security controls and evade detection.

The technical details of the evasion techniques are complex, but the lessons for the CISO are clear:

  1. Traffic to a legitimate website is not always legitimate traffic – malware could be hiding command and control communications in traffic to reputable sites.
  2. Don’t allow direct Internet access, ever. The DNS hijacking described in the blog relies on directly sending DNS queries.
  3. File-based malware controls are being successfully evaded in the wild.

What can you do to protect your organisation from these threats? My suggestions are:

  1. Make sure you have a well-architected Internet proxy architecture that prevents direct connectivity from your network:
    • Never allow hosts other than your secure external DNS resolver to send DNS queries to the Internet. Period.
    • Record all internal DNS queries, these are a possible sign of a compromised machine.
  2. Put in place a malware detection solution that can identify multi-vector, multi-stage malware execution:
    • These attacks used legitimate, signed binaries from a known security company to load malicious code contained in other files as part of a multi-stage attack. File-oriented security controls do not detect these attacks, you need a full behavioural analytics engine to see the attack.
    • Don’t assume that a signed binary is safe. Automated analysis of code behaviour in an execution environment is critical.
  3. Ensure you can detect and block command & control traffic from compromised users, even if it is to legitimate websites:
    • Sophisticated attackers can use blogs, code repositories, even comments on social media, to send and receive command & control signals.
    • Reputation-based detection is not sufficient, you need detection and protection that can understand new command and control tactics based on automated behavioural analysis.

The attackers are evolving their attacks, are you evolving your defenses fast enough to keep them out?

Your Locker of Information for CryptoLocker Decryption

Ransomware is a particularly nasty piece of malware that takes infected machines hostage. CryptoLocker was successful at garnering multi-millions in ransom payments the first two months of CryptoLocker’s distribution, according to a recent blog by FireEye regarding the takeover of CryptoLocker infrastructure - Operation Tovar.

Operation Tovar helped tear down the infrastructure used by attackers, but there are still many instances where users are still being infected with ransomware. After the success of Operation Tovar, there were few resources available to help decrypt files that were still encrypted with the attacker’s private key.

While not particularly innovative, CryptoLocker was successful because it encrypts the files of computers it infected and then demanded a ransom for a private key to decrypt those files. The harsh reality of a situation like this is, not many people back up their data. In some cases, the backups would be encrypted if mounted to an infected machine. As a result, many of the victims felt helpless at this point, and paid the ransom - typically around $300. A simple description of the way that CryptoLocker works can be found below:

  1. CryptoLocker arrives on a victim’s machine through a variety of techniques such as spear-phishing emails or watering hole attacks.
  2. CryptoLocker then connects to randomly generated domain (via DGAs) to download a specific RSA public key.
  3. At that point, an AES-256 key is created for each file on the system.
  4. CryptoLocker then encrypts all of the supported files using the generated key from step 3.
  5. The generated key is then encrypted with the downloaded RSA public key from step 2.
  6. And finally, the AES-key is written to the beginning of the encrypted files, thus requiring the private key to decrypt.
crypto1

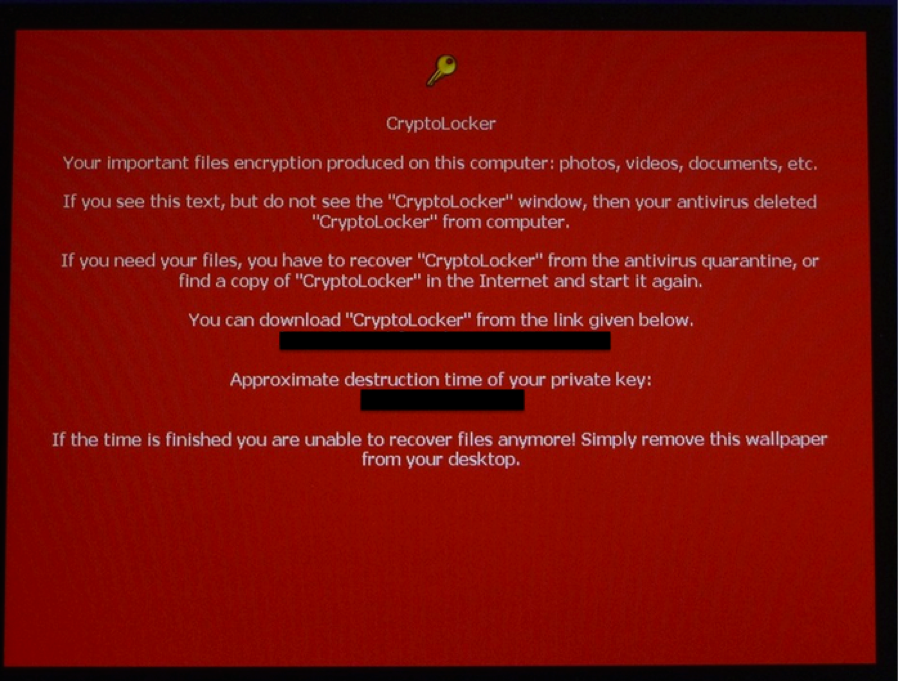
Figure 1: Screenshot of victim machine infected with CryptoLocker

Not all CryptoLocker variants are created equal. There are several copycats and hybrid versions of Crytpolocker that exist, ranging from programs like CryptoDefense, PowerLocker, TorLocker and CryptorBit, to variants that are not necessarily named but have modified functionality, such as using Yahoo Messenger as a propagation technique.

Decryption Assistance

To help solve the problem of victims’ files still being encrypted, we leveraged our close partnership with Fox-IT. We developed a decryption assistance website and corresponding tool designed to help those afflicted with the original CryptoLocker malware. Through various partnerships and reverse engineering engagements, Fox-IT and FireEye have ascertained many of the private keys associated with CryptoLocker. Having these private keys allows for decryption of files that are encrypted by CryptoLocker.

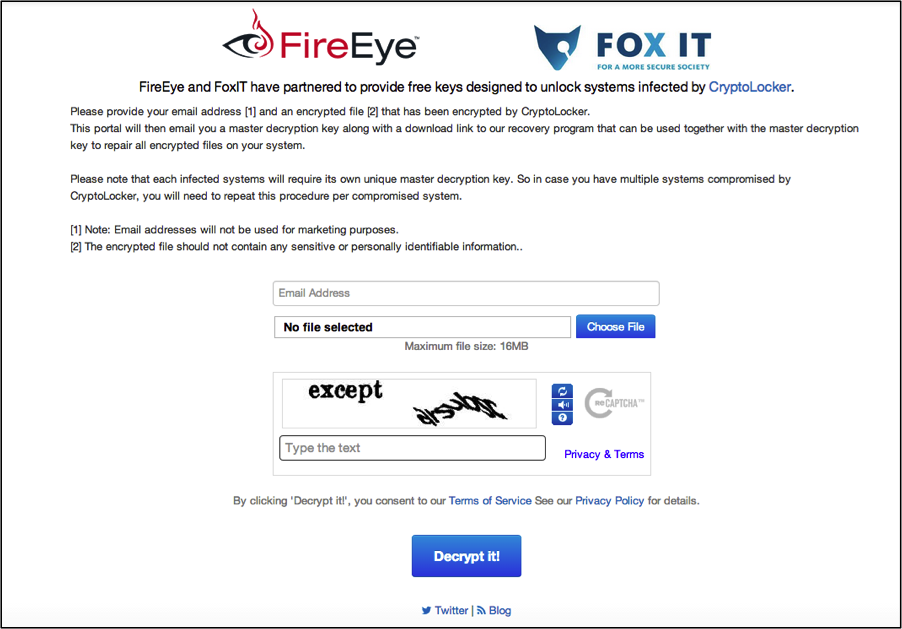
FireEye and Fox IT have created a webpage, https://www.decryptcryptolocker.com, where a user can upload an encrypted CryptoLocker file. Based on this upload, the user will be provided with the option to download a private key that should decrypt their affected files. The site also provides instructions on how to apply this key to the files encrypted by CryptoLocker to decrypt those files.

To use the site, simply upload an encrypted file without any confidential information. (Please keep in mind, we will not permanently store, view, or modify your file in any fashion.) Enter your email address, to ensure the private key associated with the file is sent to the correct individual. Ensure you enter the correct number or phrase in the Captcha entry field.

crypto2

Figure 2: Screenshot of https://www.DecryptCryptoLocker.com

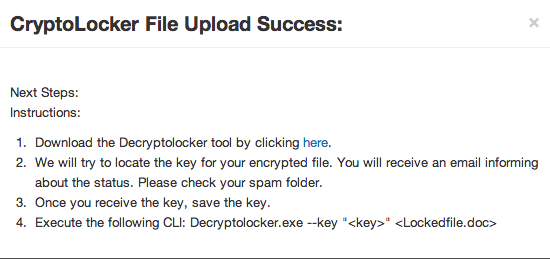
After clicking “Decrypt It!”, you will be presented with instructions to download the Decryptolocker.exe tool from https://www.decryptCryptoLocker.com (Figure 3). In addition, your private key will be sent to the email addresses specified.

crypto32

Figure 3: DecryptCryptoLocker decryption result page

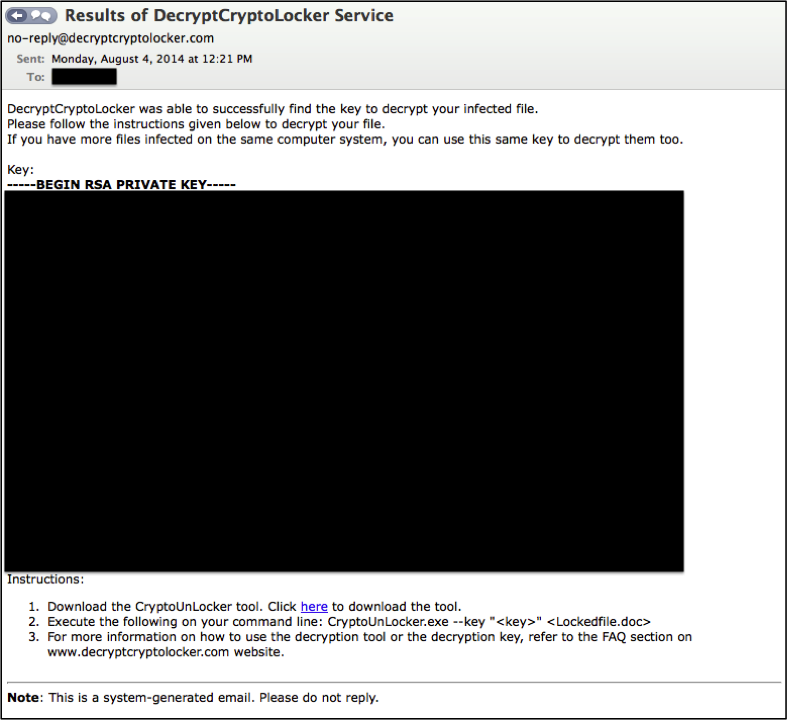
After receiving the email (Figure 4), you will then select the key and utilize it in conjunction with Decryptolocker.exe.

crypto4

Figure 4: Email containing private key

At this point, the user opens a Windows Command Prompt, and browses to the directory of the Decryptolocker.exe tool and the locked file. (Please note that the directory of the locked file must be specified if the file is not local to the tool’s directory.) The user must enter the command exactly as specified on the successful decryption page. The command structure should be used as the following:

Decryptolocker.exe -key “<key>” <Lockedfile.doc>

Upon successful execution of the tool, the user should be presented with a prompt indicating decryption was successful (Figure 5).

crypto5

Figure 5: Successful decryption of File1-1.doc

Conclusion

Operation Tovar made a clear impact on the distribution of and infection of machines by CryptoLocker. However, there have been no known avenues available designed to help users get their encrypted files back without making significant payments to those responsible for infecting machines in the first place. While the remediation of infected machines can be somewhat difficult, hopefully with the help of https://www.decryptCryptoLocker.com and Decryptolocker.exe, we can help you get back some of the valuable files that may still be encrypted.

As always, to help prevent a threat like this from affecting you and your data, ensure you backup your data. Ideally, this would be done in at least two locations: One would be on premises (such as an external hard drive), and the other would be off premises (such as cloud storage).

FAQ

Are all encrypted files afflicted with CryptoLocker decryptable with this tool?

We believe we recovered everything the from the CryptoLocker database. However, we are aware that there could be a limited data chunk that could be missing which is related to either the takedown or interruptions of the CryptoLocker backend infrastructure. As a result, certain files may not be decryptable. Also, new variants of CryptoLocker may be released at any time, and the tools we discuss here or have made available may not be able to decrypt files infected with these more recent variants.

Does this tool work against CryptoLocker variants?

There are several variants of CryptoLocker, all functioning in different ways. While these variants do appear similar to CryptoLocker, this tool may not be successful in all decryption processes because of code and functionality variances.

Does any of our data get stored by FireEye or Fox-IT?

Under no circumstances does personal data get stored, processed or examined by FireEye or Fox-IT when using this tool.

Is this service free?

The Decryptolocker.exe tool is available at no cost via the website to anyone that has been compromised with CryptoLocker.

How can I use the Decryptolocker.exe tool?

The Decryptolocker.exe tool is designed to perform a few different types of functions. Here are some examples of various prompts you can enter, depending on the result you would like to obtain.

1) If you would like to test a file if it is encrypted with CryptoLocker, you can enter:
Decryptolocker.exe -find File1.doc

2) If you would like to find all files encrypted with CryptoLocker in a directory, you can enter:

Decryptolocker.exe -find -r “C:\FolderName”

Note: Remember to include the “-r”

3) If you would like to decrypt a file encrypted with CryptoLocker, you can enter:

Decryptolocker.exe -key “<your private key provided in email>” File1.doc

4) If you would like to decrypt all files in a folder, you can enter:

Decryptolocker.exe -key “<your private key provided in email>” C:\FolderName\*

Note: Remember to include the “*” at the end

5) If you would like to decrypt all the files in a folder or drive recursively, you can enter:

Decryptolocker.exe -key “<your private key provided in email>” -r C:\

Note: Decryptolocker.exe creates a backup of all encrypted files in the same directory before writing the decrypted file. If you do not have enough space for these files, then the prompt may not execute, and your computer may run more slowly. Ensure you have sufficient file space before proceeding.


Disclaimers

There are several variants of CryptoLocker, all functioning in different ways. While these variants do appear similar to CryptoLocker, the tools discussed here may not successfully decrypt files encrypted by every variant because of differences in the programs or for other reasons. Also, while we have many unlocking keys, there is a possibility that we will be unable to decrypt your files.

References


https://www.fireeyesolution.com/blog/technical/2014/07/operation-tovar-the-latest-attempt-to-eliminate-key-botnets.html

http://blog.fortinet.com/A-Closer-Look-at-CryptoLocker-s-DGA/

https://www.fox-it.com/en/

Black Hat USA 2014: The Ultimate Cybersecurity Event

Black Hat USA is about to return for its 17th year in Las Vegas, NV. The show will bring together the brightest minds in the world of cybersecurity for a six-day period where learning, networking, and skill-building top the activity list. FireEye will be there in full force.

Here is what you need to know:

  • Be on the Look Out: FireEye and Mandiant will have a presence at the conference in booths 411 and 246, respectively. You’ll be able to watch live demos, attend presentations, and get the latest updates on our full platform of technologies and services.
  • Jump into the Trenches: Join FireEye CTO Dave Merkel on Thursday, August 7 from 1-2PM for his insightful presentation “Lessons from the Trenches: Advanced Techniques for Dealing with Advanced Attacks” which will review the latest approaches attackers are using to compromise organizations and, more importantly, what the most innovative security teams are doing to stay ahead. Mr. Merkel will be drawing on data and anecdotes from hundreds of organizations, and will outline how leading security teams have reorganized, re-architected and realigned their security strategies.
  • Take a Practical View: Visit the FireEye booth (411) for ongoing presentations with a focus on various case studies that can be applied to everyday activities. Presentations will be interactive and include audience responses.
  • View Live Demonstrations: FireEye will have eight demo stations networked to live products and solutions to recreate real and recognizable environments.
  • Come out and Party: Join the FireEye crew for an event co-sponsored by Rapid7 on Wednesday, August 6 at XS Nightclub in Wynn/Encore. Register for the party here!
  • M After Dark: There is nothing quite like Mandiant’s “M After Dark” party, which will take place on August 5, from 7-9PM at the Eye Candy Sound Lounge at Mandalay Bay. Click here for registration information.

We hope to see you in Las Vegas the week of August 2 through August 7. If you are unable to attend, check back on the blog for insights from the conference.


Security as a Differentiator: Investis Partners With FireEye Managed Defense to Offer Its Clients the Very Best in Cybersecurity

This is a contributed post from Alex Booth, COO, Investis

As a provider of digital corporate communication services to many of the world’s leading companies, information security is of critical importance to us here at Investis. In order to be the world’s safest platform for managing digital communications and hosting corporate sites, we wanted the strongest security partner in the business. As COO of Investis, this was a critical decision which is why I wanted to share the reasons we chose FireEye Managed Defense. To give you the short version, though, the choice was easy - the long version of which you can see in the video below or get a synopsis of in this post…

We are an ISO 27001 certified company and a member of CISP, the UK government’s cybersecurity information partnership. We believe you can never take security too seriously, especially in a digital landscape with increasingly sophisticated cybercrime. With that in mind, we wanted the most advanced solution to protect our environment and clients, and FireEye was the perfect partner to help us safeguard against advanced threats.

FireEye is the cybersecurity partner of choice for many of the US’s largest firms and its subsidiary, Mandiant, was selected by the UK Government Communications Headquarters (GCHQ) as one of four vendors certified to respond to cybersecurity attacks targeting the UK’s national infrastructure.

As a result of an on-site assessment by Mandiant consultants, we chose to augment our security team with the FireEye Managed Defense service.

We are looking forward to working with the great team over at FireEye to ensure we offer our clients the very best in cybersecurity.

US GAO Report Highlights Incident Response Shortcomings

On May 30th, 2014, the US Government Accountability Office (GAO) released a report titled “Information Security: Agencies Need to Improve Cyber Incident Response Practices.” GAO conducted its research by randomly selecting six government agencies, then selecting a statistically significant number of incident reports (40 from each organization), documented during 2012. GAO then evaluated how the agencies performed, based on the reports. GAO compared the documented incident response actions to requirements set by the Federal Information Security Management Act of 2002 (FISMA) and National Institute of Standards and Technology (NIST) Special Publication 800-61, Computer Security Incident Handling Guide. The results were surprising and I will explain the significance of several excerpts in this post.

First, “agencies had recorded actions to halt the spread of, or otherwise limit, the damage caused by an incident in about 75 percent of incidents government-wide. However, agencies did not demonstrate such actions for about 25 percent of incidents government-wide.”

This comment references the need to contain an intrusion. If a government agency fails to completely contain an intrusion, any gaps leave the adversary freedom of maneuver. He can exploit the containment failure to proliferate to other systems and remain in control of an organization’s systems. Anything less than 100% containment is essentially 0% containment.

Second, “for about 77 percent of incidents government-wide, the agencies had identified and eliminated the remaining elements of the incident. However, agencies did not demonstrate that they had effectively eradicated incidents in about 23 percent of incidents.”

This comment references the need to remove an intruder from a compromised organization. Similar to the need for 100% containment, one must also achieve 100% removal in order to completely frustrate the adversary. If an adversary retains access to even one system, he can rebuild his position and retake control of the victim.

Third, “agencies returned their systems to an operationally ready state for about 81 percent of incidents government-wide. However, they had not consistently documented remedial actions on whether they had taken steps to prevent an incident from reoccurring. Specifically, agencies did not demonstrate that they had acted to prevent an incident from reoccurring in about 49 percent of incidents government-wide.”

This comment describes the need to learn from intrusions and implement remediation. If a victim fails to make the environment tougher for the adversary, the intruder will likely return using the same techniques that he utilized to first gain access.

Finally, a search of the entire GAO report for the word “strategy” produced zero hits. Beyond being disappointed by the three excerpts I highlighted above, I am dismayed to not hear GAO discuss the need for a security strategy for organizations. Incident response is not a technical action. IR should be part of a business process, done as part of an operation that implements a strategy understood and approved by the highest levels of management. Furthermore, the GAO report did not really evaluate the consequences of the three documented failures and the lack of concrete security strategies. Had GAO taken that step, they might have concluded that the agencies continue to face severe security challenges.