Network Security
Defend your network, data, and users with the fastest, most reliable cyber-attack protection available
FireEye Network Security is an advanced threat protection and breach detection platform that provides industry leading threat visibility and protection against the world’s most sophisticated and damaging attacks. By leveraging FireEye’s unique technologies and threat intelligence, FireEye Network Security detects what other security solutions miss, providing holistic security from the perimeter to the network core.
Ideal for next-generation networks that need flexible and scalable deployment options, FireEye Network Security offerings provide strong security for a myriad of environments and customer needs.
Video
Flexible Network Security
FireEye SmartVision
Detect suspicious lateral network traffic within your network
FireEye SmartVision is a network traffic analysis (NTA) solution that detects suspicious lateral traffic within an enterprise network. It is comprised of an advanced correlation and analytics engine, a machine learning module to detect data exfiltration attempts, and is bolstered by 120+ intrusion detection rules that identify weak indicators of compromise.
Unlike other network security solutions that sit at the perimeter, FireEye SmartVision can be deployed all throughout the network – at the core, across network segments, or in front of key servers and IT assets.
Once deployed, FireEye SmartVision Edition identifies unique threat actions across the lateral attack cycle, further reducing post-breach dwell time and risk of loss.
Features
- Detects suspicious lateral network traffic
- Detonates objects over SMB/SMB2 protocols
- Visualizes alerts to quickly triage events
- Supports extensive metadata protocols
- Complements existing FireEye Network Security deployments
- Integrates with FireEye Helix
Benefits
- Decreases time to detect post-breach activities
- Provides flexibility to scale through the entire network
- Enables visibility into network segmentation initiatives
- Improves network forensics and incident response
- Reduces attacker dwell time
Network + Email
1 + 1 = 3 with Network and Email Security.
Find out how you can
see the bigger picture, detect blended
attacks, and respond more effectively.
Network Security
FireEye Network Security is designed for high-performance, pervasive and consistent protection against threats across your organization with integrated security workflow and actionable contextual intelligence. It enables you to:
- Accurately detect and immediately stop attacks that evade other security devices, including file-based sandboxes
- Understand and prioritize critical alerts with reliable execution evidence and contextual insights
- Proactively defend and investigate threats with tactical intelligence from FireEye or a third party using the Structured Threat Information eXpression (STIX) format as well as contextual and strategic threat intelligence
- Deploy Network Security with integrated all-in-one hardware appliances or with a scalable and flexible on-premise or cloud-based distributed model
- Future-proof your investment with an extensible, modular architecture
- Provide your Microsoft Windows and Apple OS X users with the same level of threat protection
- Achieve quick protection with machine-, attacker- and victim-based intelligence applied as updates to your defenses every 60 minutes
- Shorten the solution payback period by eliminating the operational cost of triaging alerts manually
- Integrate and automate your security workflow to easily prioritize, investigate and respond to alerts across different threat vectors
Network Security Requirements
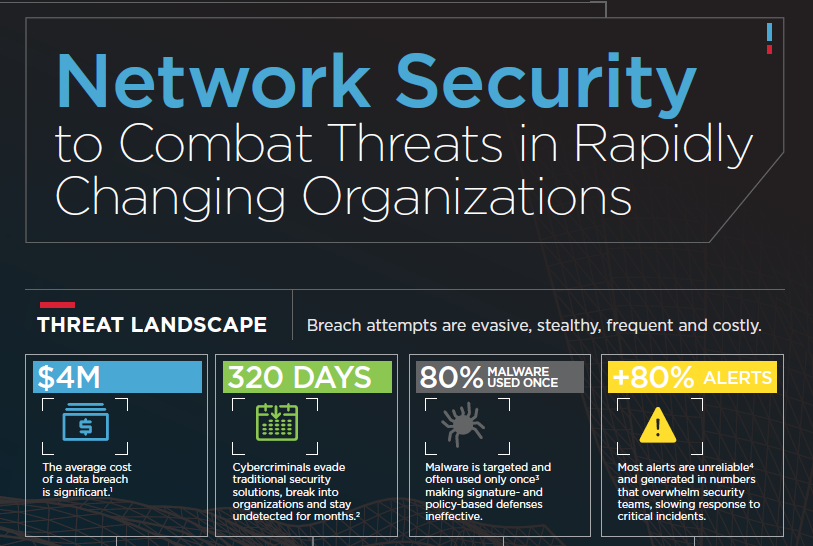
Address IT transformations and the evolving threat landscape to help ensure fast, cost-efficient, consistent detection and response.
The Value of FireEye Network Security
Delta Testing Report
FireEye NX Achieves 99% Detection Rate

Frost & Sullivan Report
Advanced Malware Sandbox Market Analysis
Forrester Study
The Total Economic Impact of FireEye Network Security
Article
Network World NX Review
How FireEye Network Security Helps
eBook
The Assault on Small and Midsize Organizations
eBook
Success and Failure in Cyber Security
eBook
Network Security, A Buyer's Guide
Solution brief
High Performance NX Series Solution
Solution brief
Network Security
Whitepaper
The Business Case for an Advanced Security Solution
TESTIMONIAL
“When it comes to detecting and preventing advanced attacks, the power of FireEye MVX technology has no competition.”
- Wahid Hammami, Chief Information Officer
| Product Feature | Benefit | FireEye Network Security |
|---|---|---|
| Detect advanced, targeted and evasive threats traditional security solutions miss | ||
| Signature-less threat detection (MVX service) Signature-less threat detection (MVX service) | Detects multi-flow, multi-stage, zero-day, polymorphic, ransomware and other advanced attacks Detects multi-flow, multi-stage, zero-day, polymorphic, ransomware and other advanced attacks |
|
| Real-time and retroactive detection Real-time and retroactive detection | Detects known and unknown threats in real time while also enabling back-in-time detection of threats Detects known and unknown threats in real time while also enabling back-in-time detection of threats |
|
| Multi-vector correlation Multi-vector correlation | Automates validation and blocking of attacks across multiple vectors Automates validation and blocking of attacks across multiple vectors |
Email (on-premise or cloud),
Email (on-premise or cloud), file and endpoint
file and endpoint |
| Multi-OS, multi-file and multi-application Support Multi-OS, multi-file and multi-application Support | Supports heterogeneous endpoint environments for a wide range of applications Supports heterogeneous endpoint environments for a wide range of applications |
|
| Hardened hypervisor Hardened hypervisor | Provides evasion proofing Provides evasion proofing |
|
| Rapidly respond and contain the impact of intrusions | ||
| Real-time inline blocking Real-time inline blocking | Immediately stops attacks Immediately stops attacks |
|
| Signature-based IPS Detection Signature-based IPS Detection | Automates and accelerates triaging of traditionally noisy alerts to eliminate overhead Automates and accelerates triaging of traditionally noisy alerts to eliminate overhead |
|
| Riskware Detection Riskware Detection | Categorizes critical and non-critical malware to prioritize response resources Categorizes critical and non-critical malware to prioritize response resources |
|
| Integrated security workflows Integrated security workflows | Pivots from detection to investigation and response Pivots from detection to investigation and response |
Endpoint Forensics Enterprise Forensics |
| Actionable contextual intelligence Actionable contextual intelligence | Accelerates containment of advanced threat with in-depth information about the attack and attacker Accelerates containment of advanced threat with in-depth information about the attack and attacker |
|
| High Availability (HA) High Availability (HA) | Provides resilient defense Provides resilient defense |
|
| Continually adapt to the evolving threat landscape | ||
| Real-time threat intelligence sharing Real-time threat intelligence sharing | Globally-shares real evidence to immediately block previously unknown attacks and accelerate response Globally-shares real evidence to immediately block previously unknown attacks and accelerate response |
|
| Custom and third-party threat intelligence (STIX)* Custom and third-party threat intelligence (STIX)* | Allows ingestion of non-FireEye indicators into the intelligence-driven analytics engines Allows ingestion of non-FireEye indicators into the intelligence-driven analytics engines |
|
| Strategic threat intelligence Strategic threat intelligence | Enables a proactive assessment of threat landscape changes and empowers a lean-forward security posture Enables a proactive assessment of threat landscape changes and empowers a lean-forward security posture |
|
* Only supported on fourth-generation (NX x4xx) and newer appliances configured in the integrated mode.
Our network security solutions will help you:
- Minimize the risk of costly breaches by immediately detecting and stopping attacks hiding in Internet traffic
- Gain attack context with intelligence on adversaries, breach victims, and insights from 5,000+ customer deployments
- Have real-time visibility into known and unknown threats with 14 million + virtual analyses per hour
- Reduce your workload and operational expenses by focusing on real attacks with the lowest false positive rate
- Benefit from Department of Homeland Security SAFETY Act certification by gaining liability protection and greater confidence in your security
- Future proof your investment by scaling security with your business, whether in the on-premise or in the cloud
FireEye network security by the numbers:
- 50%: The percentage of zero-day exploits we have detected in the wild — greater than all other security companies combined.
- 99.14% vs. 33.62%: Our attack detection rate compared that of the next highest performing technology.
- 152% and 9.7 months: The ROI you can expect and the estimated amount of time it will take for you to realize payback on your investment.
Resources
Network Deployment & Integration
Rapid and effective integration into your security environment
Video
Flexible Network Security
Literature
FireEye International Literature
Ready to get started?
Ask about FireEye solutions, implementation or anything else. Our security experts are standing by, ready to answer your questions.
