Government agencies are under constant attack, targeted by increasingly sophisticated and well-funded cybercriminals and nation-states. To protect against state-sponsored espionage, data breaches, and advanced persistent threats (APTs), federal, state, and local agencies must fill the security gap left by traditional defenses such as next-generation firewalls, IPS, anti-virus, and gateways. These defenses rely heavily on malware binary signatures and are no match for well-funded adversaries employing a new generation of dynamic, stealthy threats.
Government agencies face a unique challenge. They must balance compliance mandates and limited budgets with proactive IT security. Federal agencies must comply with Federal Information Security Management Act (FISMA) regulations and protect themselves from advanced cyber attacks. State and local agencies must protect critical assets such as social security numbers and utility infrastructures with limited budget and resources. Spurred by FISMA compliance mandates and NIST directives to embrace risk management through continuous monitoring and attack-based metrics, as well as the increasing demands for advanced threat protection, government agencies are turning to FireEye for game-changing technologies and services that offer unmatched protection. The FireEye platform – a combination of FireEye technology, rich actionable threat intelligence, and world-class support and services – offers governments a next-generation security solution to combat advanced cyber threats.
Government Solution Overview
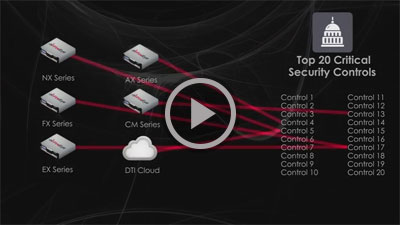
The FireEye platform:
- Protects critical government assets against advanced targeted attacks across multiple threat vectors such as Web, email, file shares, and mobile
- Provides a detonation chamber, the FireEye Multi-Vector Virtual Execution (MVX) engine. This virtual-machine-based security engine is built from the ground up to provide dynamic, real-time analysis of malware to defend against advanced threats
- Enables cyber operations to be proactive versus reactive saving time and resources
- Addresses key compliance controls in National Institute of Standards and Technology (NIST) 800-53
- Maps to the critical controls listed in the SANS (Council on Cyber Security) 20 Critical Security Controls for Effective Cyber Defense
- Integrates with SIEM to help compliance teams collect and store audit information relevant to security events to meet long-term data retention and FISMA quarterly reporting requirements
- Offers Oculus Continuous Monitoring, a subscription service that provides around-the-clock threat monitoring and proactive alerts on APTs and industry-specific threats
Resources
- Solution Mapping Guide: FISMA and SANS Critical Security Controls
- Report: FCW Continuous Monitoring Report
- White Paper: Federal CISO Dilemma White Paper
- Blog: FireEye Report: World War C
- Blog: Former CIA CISO on Nation-State Security Challenges
- Blog: Poison Ivy: Assessing Damage and Extracting Intelligence
- Video Testimonial: Robert Lentz, Former CISO of the Department of Defense
- Webcast and Use Case: SANS WhatWorks in Detecting and Blocking Advanced Threats at a Large Research Organization
- Backgrounder: Government Top Target for APT Attacks