FireEye as a Service
Extend your security operations with industry-leading expertise, threat intelligence and technology
Technology alone will not defeat persistent, well-funded attackers. Yet security teams often lack the time, in-depth knowledge of adversary behaviors, and investigative expertise required to detect today’s increasingly sophisticated threats. Consequently, many organizations never really know to what extent they’ve been compromised.
FireEye as a Service is a managed detection, investigation and response service that provides battle-savvy security experts, equipped with timely, relevant threat intelligence to detect, investigate and remediate threats early in the attacker lifecycle.
Video
Answers, Not Alerts
Powered by professionals
Watch our FireEye as a Service experts describe their proactive approach to hunting for threats in your environment.
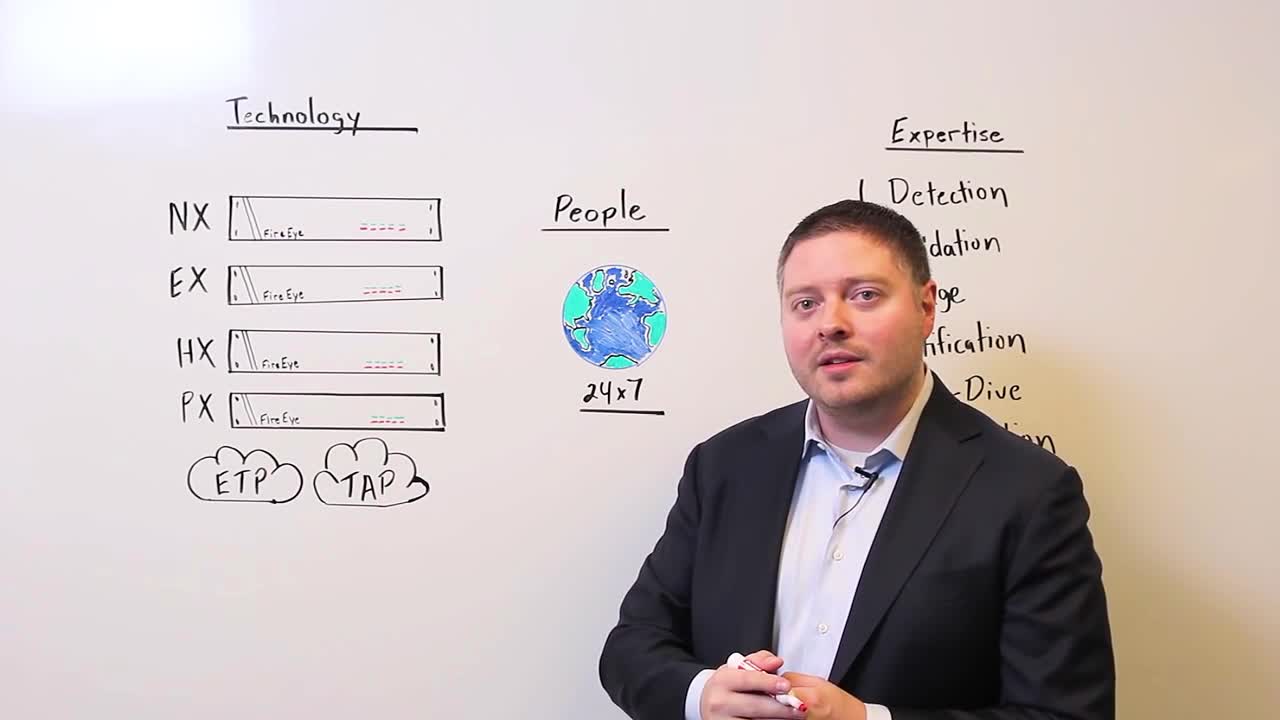
The FireEye as a Service Architecture
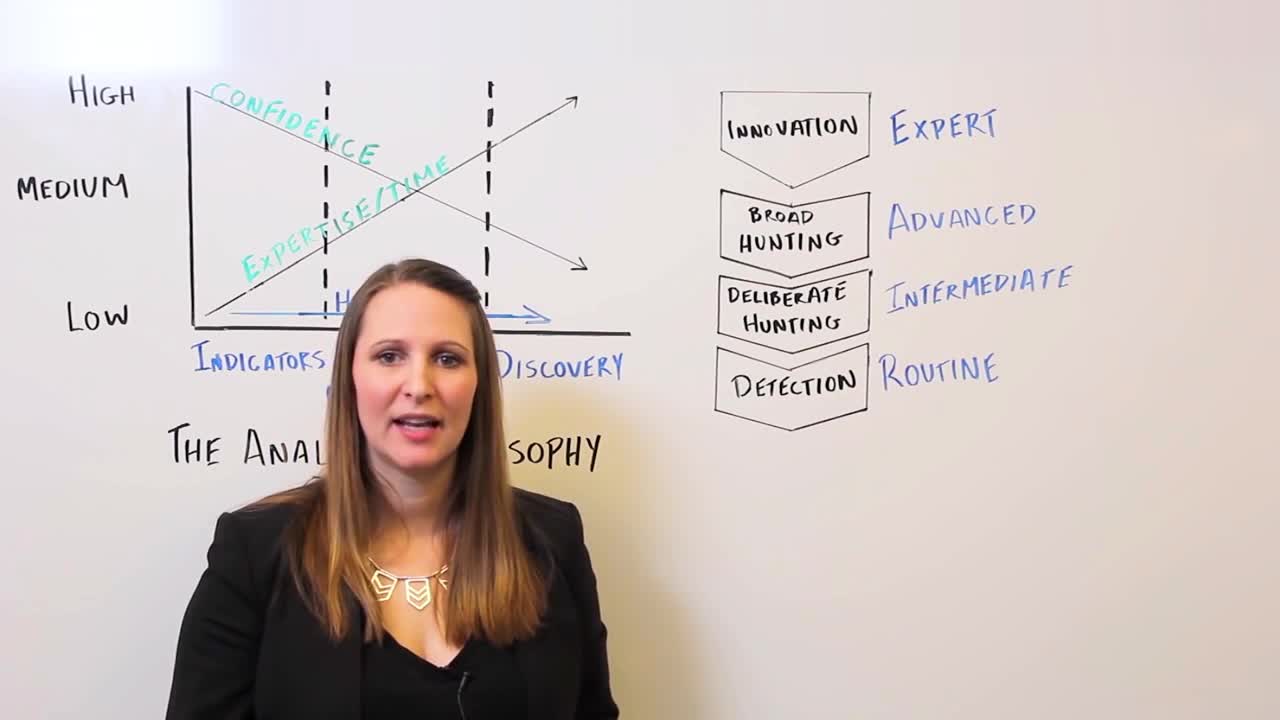
Hunting for Threats in FireEye as a Service
FireEye as a Service On-Boarding
Early detection reduces business risk
Detect threats that matter
Gain real-time visibility into evolving threats within and outside your organization.
- Adaptive detection, informed by adversary, victim and machine intelligence
- Experts proactively hunt for anomalies that indicate hidden attacker activity
Investigate thoroughly
Quickly assess risk with detailed compromise assessments from our remote incident investigation team.
- Proprietary investigation methods reveal signs of intrusion and quickly assign severity
- Gain insights into how attackers operate – their evolving tactics, tools and procedures
Respond confidently and correctly
Prescriptive recommendations from industry-leading experts for faster threat response.
- Contextually rich, incident-specific threat intelligence informs risk assessment
- Expert remediation recommendations provide customized, practical advice for quickly responding to threats
TESTIMONIAL
“The FireEye suite of technologies combined with FireEye as a Service provides a level of coverage and visibility that my organization could not afford to duplicate by other means (e.g. hiring the necessary staff).”
- C.L., Information Security Manager for a mid-sized US manufacturer
FireEye as a Service features
Premium security expertise to augment your security organization – within your budget

Investment protection
Leverage existing investments, whether on premise, in the cloud or in hybrid environments.
Adaptive, intuitive analytics
Discover non-malware-based threats by exposing hidden patterns and anomalies in data.
Proactive immunity
Receive hourly, machine-ready threat intelligence updates on new attacker methods.
One-click containment
Isolate compromised systems instantly to reduce the impact of breaches.
Continuous vigilance
Use a follow-the-sun workflow to ensure seamless handoff of in-progress investigations.
Global scale
Take advantage of seven Advanced Threat Response Centers (ATRCs) operating worldwide.
Compliance dashboards and widgets
Easily visualize and report on data to adhere to PCI, HIPAA and other requirements.
Engagement managers
Facilitate additional support such as analysis of malware samples, in-depth forensic analysis or optional on-site incident response.
How FireEye as a Service works
FireEye as a Service managed detection, investigation and response service. It extends your security team with a combination of experts, technology and intelligence to detect and investigate attacks on your network.
- FireEye as a Service leverages your existing investments in both FireEye and third party technology to provide real-time visibility across the enterprise, including your most remote locations.
- FireEye’s expert threat analysts extend beyond traditional security monitoring, using proprietary techniques powered by adversary, victim and machine-based threat intelligence to detect, investigate and proactively hunt for previously undetected threats.
- When we validate signs of compromise, we notify you immediately and deliver a full investigative report that provides context on the threat to inform an effective response.
- In some cases, we recommend the immediate quarantine of affected systems to prevent lateral movement of attack.
- If required, FireEye incident responders with forensic expertise can also help you resolve incidents quickly and assess impact for prompt, accurate disclosure.
Related resources
eBook
Expertise On-Demand: How to Enhance Your Security Team
White paper
Community Protection: Security in Numbers
White paper
Cyber security then and now
White paper
Building a business case for FireEye as a Service
White paper
Closing the expertise gap
Use case
Clandestine Wolf:
FireEye as a Service in action
Video series
Meet the People Behind FireEye as a Service
Video
The FireEye as a Service portal
Related products and services
FireEye Helix
Simplify, integrate and automate security operations to stop threats faster.
Incident Response Services
Resolve security incidents quickly, efficiently and at scale.
Security Program Assessment
Improve your security posture by evaluating your information security program.
Ready to get started?
Ask about FireEye solutions, implementation or anything else. Our security experts are standing by, ready to answer your questions.
