Uncategorized (UNC)
Threat Groups
An uncategorized (UNC) threat group is a cluster of cyber intrusion activity which includes observable artifacts such as adversary infrastructure, tools, and attack patterns, but is not yet classified as an advanced persistent threat (APT) or financially motivated (FIN) group.
As more artifacts and analysis are collected on these UNC groups, Mandiant Threat Intelligence may merge these activity sets with other UNC groups or reclassify them during the graduation process as a temporary (TEMP), APT or FIN group.
FREE Cyber Threat Intelligence
Get more insights about UNC Groups as we uncover them.
UNC2452
UNC2452 is a sophisticated group that has targeted government and private sector entities worldwide. They have employed many unique capabilities, including gaining initial access through a software supply chain vulnerability.
After gaining access to a victim network, UNC2452 has a light malware footprint, often using legitimate credentials to access data and move laterally. The U.S. government attributed the SolarWinds supply chain compromise which we track as UNC2452 to the Russian Foreign Intelligence Service (SVR). Mandiant Threat Intelligence assesses that UNC2452 activity aligns with nation-state priorities broadly and that the group’s targeting patterns are consistent with Russian strategic interests.
- First Seen: December 2020
- Source Region: Russia
- Targeted Regions: 12
- Motivation: Espionage
- Associated Malware: BEACON, RAINDROP, SUNSHUTTLE, TEARDROP
- Other actors merged into this group: 6
- Relevant Reports Available in Mandiant Advantage: 21
UNC1878
UNC1878 is a financially motivated group that monetizes their intrusions by extorting their victims following the deployment of RYUK ransomware. As of September 2020, Mandiant has increasingly observed KEGTAP campaigns as the initial infection vector for UNC1878 operations; previously, UNC1878 used TrickBot for initial access. UNC1878 has used various offensive security tools, most commonly Cobalt Strike BEACON, along with legitimate tools and built-in commands such as PSEXEC, WMI, and BITSadmin.
- First Seen: September 2020
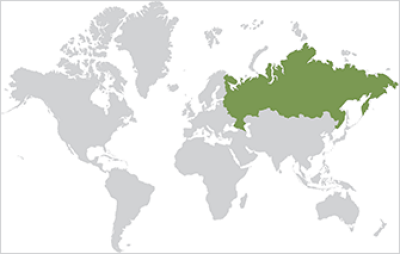
- Source Region: Russia
- Targeted Regions: 16
- Motivation: Finacial Gain
- Associated Malware: ANCHOR, BEACON, BLUESPINE, CONTI + 23 MORE
- Other actors merged into this group: 11
- Relevant Reports in Mandiant Advantage: 22
Additional resources
UNC1945
UNC1945 is a group that has been observed targeting a number of organizations in the telecommunications, financial, and business services industries since at least early 2018. The goal of UNC1945 is currently unknown because Mandiant has not been able to observe the activities that followed UNC1945 compromises. Based on available information Mandiant has not been able to assess a general location that the group operates from.
- First Seen: August 2020
- Source Region: Unknown
- Targeted Regions: Unknown
- Motivation: Unknown
- Associated Malware: EVILSUN, LEMONSTICK, LOGBLEACH, OPENSHACKLE, SLAPSTICK
- Other actors merged into this group: 1
- Relevant Reports in Mandiant Advantage: 3
Additional resources
UNC2529
UNC2529 is a well-resourced and experienced group that has targeted multiple organizations across numerous industries in a global phishing campaign. They have used phishing emails containing inline links to malicious URLs hosting DOUBLEDRAG malware, a highly obfuscated Javascript downloader. UNC2529 has also used weaponized Microsoft Excel documents as a first stage downloader. DOUBLEDRAG attempts to download a second-stage obfuscated PowerShell memory-only dropper, which Mandiant tracks as DOUBLEDROP, that will launch a backdoor into memory. This third-stage backdoor is tracked as DOUBLEBACK. UNC2529 displayed indications of target research based on their selection of sender email addresses and subject lines which were tailored to their intended victims. Although Mandiant has no data on the objectives of this threat actor, their broad targeting across industries and geographies is consistent with a targeting calculus most commonly seen among financially motivated groups.
- First Seen: December 2020
- Source Region: Unknown
- Targeted Regions: 12
- Motivation: Unknown
- Associated Malware: DOUBLEBACK, DOUBLEDRAG, DOUBLEDROP
- Other actors merged into this group: 0
- Relevant Reports in Mandiant Advantage: 1
Additional resources
UNC2639
UNC2639 was first identified exploiting multiple zero-day vulnerabilities in Microsoft Exchange in early March 2021. This actor uses these vulnerabilities to deploy webshells including CHINACHOP.
- First Seen: March 2021
- Source Region: Unknown
- Targeted Regions: 2
- Motivation: Unknown
- Associated Malware: CHINACHOP
- Other actors merged into this group: 0
- Relevant Reports in Mandiant Advantage: 6

Other Uncategorized Groups
These posts cover a large number of uncategorized threat actors, including: UNC2582, UNC2546, UNC2529, UNC26528, UNC2659, UNC2465, UNC2447, UNC1151, UNC2198, UNC2420, UNC2374, UNC2414.
August 10, 2021
UNC215: Spotlight on a Chinese Espionage Campaign in IsraelJune 16, 2021
Smoking Out a DARKSIDE Affiliate’s Supply Chain Software CompromiseMay 11, 2021
Shining a Light on DARKSIDE Ransomware OperationsMay 4, 2021
The UNC2529 Triple Double: A Trifecta Phishing CampaignApril 29, 2021
UNC2447 SOMBRAT and FIVEHANDS Ransomware: A Sophisticated Financial ThreatApril 28, 2021
Ghostwriter Update: Cyber Espionage Group UNC1151 Likely Conducts Ghostwriter Influence ActivityMarch 4, 2021
New SUNSHUTTLE Second-Stage Backdoor Uncovered Targeting U.S.-Based Entity; Possible Connection to UNC2452February 25, 2021
So Unchill: Melting UNC2198 ICEDID to Ransomware OperationsFebruary 22, 2021
Cyber Criminals Exploit Accellion FTA for Data Theft and ExtortionFebruary 16, 2021
Light in the Dark: Hunting for SUNBURSTJanuary 19, 2021
Remediation and Hardening Strategies for Microsoft 365 to Defend Against UNC2452December 18, 2020
Direct Access to Threat Intelligence With Mandiant AdvantageDecember 17, 2020
DebUNCing Attribution: How Mandiant Tracks Uncategorized Threat Actors